Get certified. Stay certified.
Defence and government contracts increasingly require proof of cyber security. We prepare suppliers for certification — gap assessment, remediation, evidence and mock assessment — then keep them compliant.
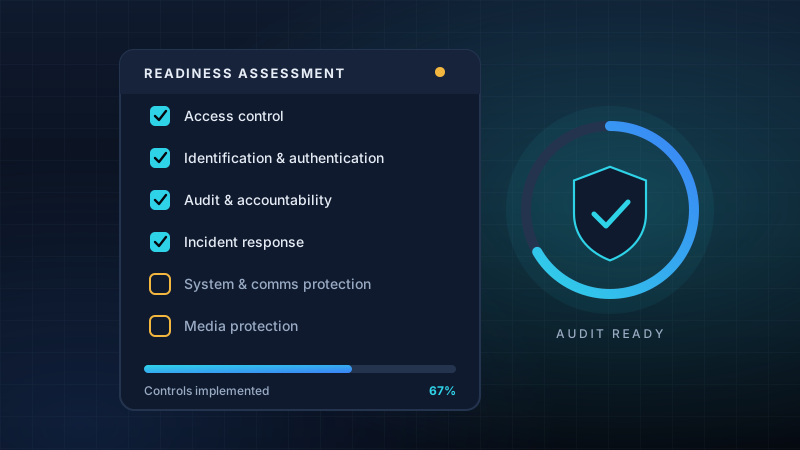
Built for suppliers to defence and government
Canada’s CPCSC program and the U.S. CMMC program both build on the NIST SP 800-171 family of controls (in Canada, ITSP.10.171). Most suppliers are small and mid-sized firms without security staff. We give them a clear, fixed-scope path from where they are today to assessment-ready.
Level 1 quick-start
Scoping, self-assessment against the foundational requirements, a fixes list and support for your attestation.
Level 2 readiness
Gap assessment across all controls, System Security Plan, remediation roadmap, evidence pack and a mock assessment.
Remediation delivery
We implement the fixes: identity and MFA, logging, policies, secure data enclaves and device management.
Compliance-as-a-service
Ongoing evidence upkeep, access reviews, annual affirmations and a fractional security lead.
Supplier readiness programs
For prime contractors: group programs that bring entire supply chains to the required level.
Other frameworks
ISO/IEC 27001, SOC 2 readiness, PIPEDA and provincial privacy, and sector-specific requirements.
What you can expect
- A scoped boundary that keeps certification cost under control
- A System Security Plan and evidence that assessors expect to see
- A prioritized remediation roadmap with fixed-fee options
- A mock assessment before the real one
- Continuous compliance so renewal is a non-event
Independence: Black Shield Security prepares organizations for certification. Formal Level 2 certifications are issued by accredited certification bodies; we do not certify the clients we advise.
Technologies & frameworks
Vendor-neutral recommendations based on your environment, risk and budget.
Common questions
How long does Level 2 readiness take?
Most suppliers need 6–12 months to prepare, depending on size and current maturity. Starting early avoids losing contract opportunities.
Do you offer fixed-fee projects?
Yes. Level 1 quick-starts and Level 2 readiness assessments are offered on a fixed-fee basis after a short scoping call.
We supply U.S. and Canadian programs. Can you help with both?
Yes. Because CPCSC and CMMC share the same control foundation, we build one program that serves both wherever possible.
Let’s secure what matters to you.
Tell us about your site, your systems or your compliance deadline. We reply within one business day, in English, Spanish or Portuguese.